The intelligence feedUpdated as material events develop
Analysis / Research / Guidance
The Briefing
Independent reporting on AI security, exploited vulnerabilities, and enterprise cyber risk. Built to help defenders understand what changed and what deserves action.
USB drives and other removable media still create quiet risk in 2026 because one borrowed thumb drive can bypass browser, email, and SaaS controls entirely. This practical checklist shows small teams how to limit unknown media, tighten file-transfer workflows, scan exceptions, and stop convenience from turning a plug-in habit into a breach path.
Palo Alto GlobalProtect vulnerability CVE-2026-0257 became a same-day operational story on July 21, 2026, when new reporting tied the VPN auth bypass to real Qilin ransomware intrusions. The practical lesson is that an unpatched remote-access gateway can turn into a fast path from perimeter access to domain-wide encryption.
RubyGems supply chain attack became the urgent developer-security story on July 20, 2026, when SleeperGem showed how dormant gems and an impersonated package could be used to backdoor real workstations while skipping CI. The practical lesson is that package trust now depends as much on maintainer continuity and install behavior as on download counts.
WordPress Core RCE became the operational story on July 18, 2026, when public exploit circulation pushed wp2shell from an urgent security release into a real patch-now event for internet-facing sites. The deeper lesson is that one exposed WordPress instance can still become a direct business-system risk even when no vulnerable plugin is involved.
ACR Stealer attacks became a same-day security story on July 18, 2026, when public reporting highlighted a surge in ClickFix-driven intrusions stealing browser passwords, live session tokens, and Microsoft 365 files. The real lesson is not the malware brand. It is how one copied command can turn a normal workstation into a fast path for cloud account abuse and document theft.
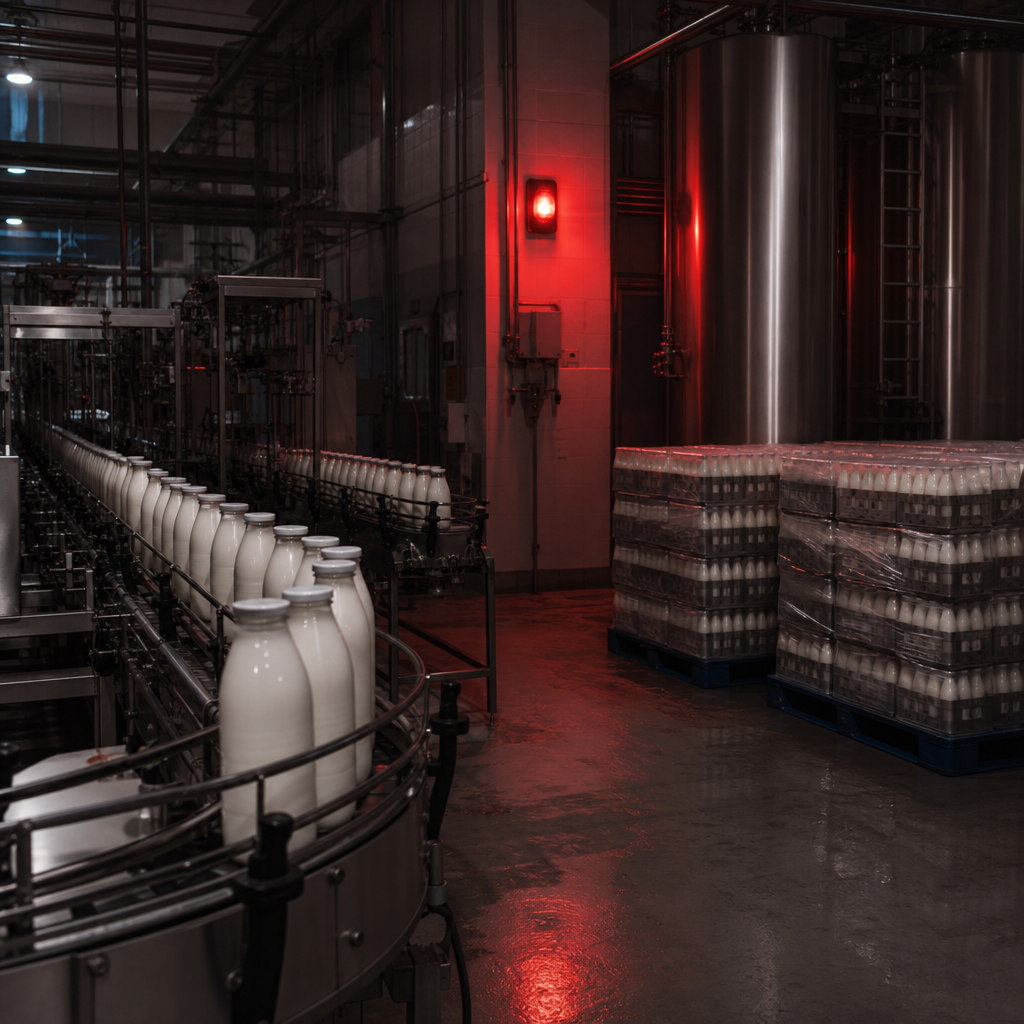
The Fairlife ransomware attack became a major July 17, 2026 cybersecurity story after Coca-Cola disclosed that production-related systems were affected and US output was temporarily suspended. The incident is a sharp reminder that when ransomware reaches plant operations, the real damage is not just encrypted files. It is lost production, strained recovery options, and a supply chain problem customers can actually feel.
AI voice cloning has made urgent phone scams more convincing for finance, support, and operations teams in 2026. This practical playbook shows small businesses how to verify high-risk calls, slow down executive impersonation, and keep voice requests from turning into payment fraud or account takeover.
Spirals ransomware became a same-day security story on July 16, 2026, when public reporting showed a new operator moving from an exposed IIS server to data theft and network-wide encryption in less than 24 hours. The bigger lesson is not the brand name. It is how quickly a reachable web server, stolen credentials, disabled defenses, and weak recovery discipline can turn into a business-stopping event.
SharePoint vulnerabilities became a same-day priority on July 15, 2026, when public reporting showed attackers actively exploiting three flaws across internet-exposed on-premises servers. For security teams, the bigger issue is not just patching one bug. It is hardening exposed SharePoint estates before stolen IIS machine keys and post-exploitation persistence turn a collaboration platform into a durable foothold.
 Cybersecurity